Why This Investigation Matters
The command-and-control model that defenders have spent two decades learning to detect rests on a foundational assumption: a human operator is making decisions, issuing instructions, and responding to feedback in something close to real time. Three malware families documented in 2025 and 2026 invalidate that assumption. ClosedQuorum, RatHat, and Carbonato each delegate tactical decisions to AI models, removing the operator from active execution. Detection logic built around human-paced C2 cadence will miss them.
I wrote this piece for Dispatch because the coverage I had seen framed AI-enabled malware primarily as an evasion upgrade. That framing understates the actual problem. Evasion is one component, but the structural change is autonomy, and the two require different defensive responses.
ClosedQuorum: A Voting Panel of LLMs
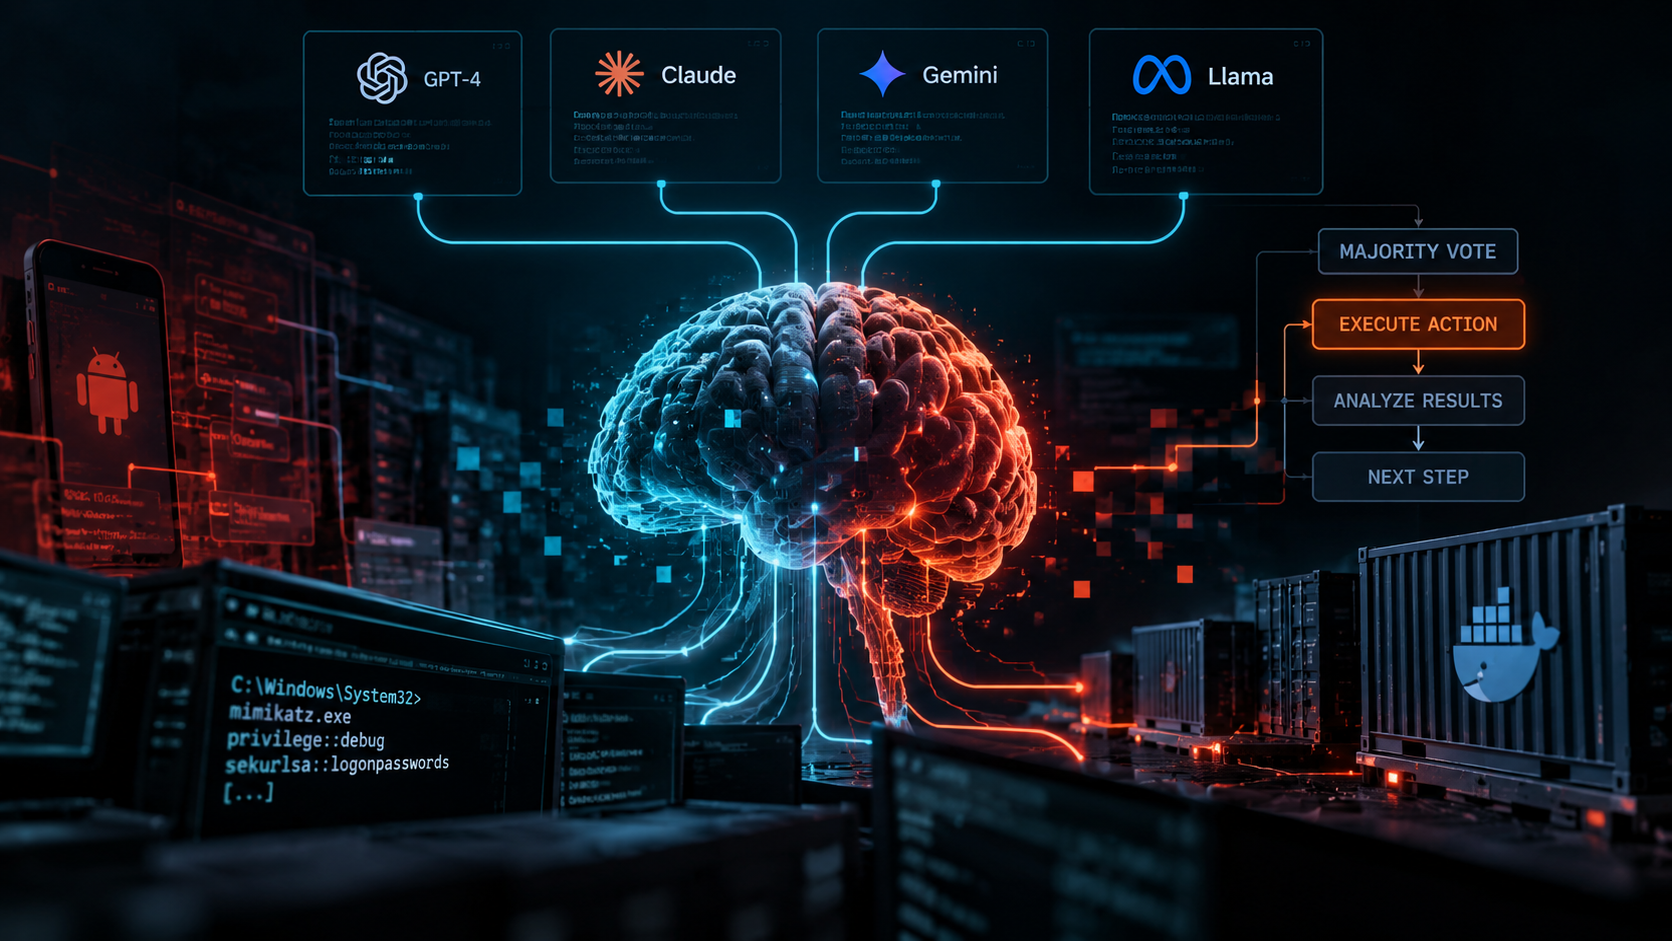
ClosedQuorum is a 16.4 MB Go-based Windows implant that convenes an internal panel of four commercial large language models: DeepSeek, Qwen, Mistral, and Google Gemini. It sends each model a system prompt identifying itself as an advanced malware strategist and requests a JSON response selecting from four actions: steal credentials, inject code, establish persistence, or move laterally. The majority vote determines execution. Ties break deterministically in DeepSeek’s favour.
Each action is operationally complete. A steal vote triggers simultaneous LSASS memory dumps, browser password sweeps across Chrome, Edge, and Firefox, and cryptocurrency wallet extraction. A persist vote creates three overlapping mechanisms at once: a Registry Run key, a scheduled task, and a WMI event subscription firing every 60 seconds via PowerShell. The implant also suppresses Event Tracing for Windows telemetry by overwriting EtwEventWrite with a return instruction, blinding Windows logging for the session. Data exits encrypted with AES-256-GCM via Discord webhooks.
The four-model voting structure has a specific defensive implication worth noting. A single provider’s content safety refusal cannot block the attack, because three remaining models can still form a plurality. Operators also use legitimate commercial API endpoints as the implicit C2 channel, which makes domain-level blocking impractical without disrupting enterprise AI tooling across the organisation.
Cisco Talos researchers, who discovered ClosedQuorum through their CAIRN toolkit, describe it as an architectural shift towards attack-chain automation. Recovered development builds contain real API credentials injected at compile time, suggesting per-operator commercial distribution rather than a research sample.
RatHat and Carbonato: The Same Logic, Different Platforms
RatHat applies the same principle to Android. Discovered by Zimperium zLabs and attributed to Chinese threat actors based on Mandarin-language LLM prompts in the binary, it abuses Android’s AccessibilityService APIs to gain ADB-level device control without root privileges. The AI component serialises the live Android Accessibility tree into XML and queries an LLM to identify UI element coordinates, extract on-screen text, and issue navigation instructions. The result is malware that can navigate any app interface dynamically, without pre-scripted flows. Traditional automation-based mobile fraud requires the attacker to anticipate every screen state. AI-driven UI navigation does not.
Carbonato extends the pattern to infrastructure, targeting Docker hosts with unauthenticated APIs exposed on port 2375. After gaining access, it deploys the Hermes Agent AI framework under a persona named GH0ST. The agent receives high-level task commands via Telegram, executes them autonomously on victim hosts, and returns results. It scans networks attached to every compromised host every five minutes for additional exposed Docker daemons, propagating without human direction. The Hermes Agent framework is not purpose-built malware. It is a repurposed AI agent platform that has appeared in other malicious campaigns, including a card-skimming operation that stole 600,000 credit card details. Commodity AI agent frameworks require minimal adaptation for offensive use.
The Autonomy Problem
Google’s Threat Intelligence Group identified five novel AI-enabled malware families in 2025, with three already observed in active operations. PROMPTSTEAL, used by APT28 against Ukrainian targets, represents the first observed instance of malware querying an LLM during live operations to dynamically generate execution commands. PROMPTFLUX uses the Gemini API to rewrite its own VBScript source code on an hourly cycle to evade detection.
Taken together, these families represent a documented escalation across a single calendar year, not a capability sitting somewhere on a threat horizon.
The dwell-time detection strategies that underpin many incident response playbooks assume human-paced attacker behaviour: reconnaissance, then a pause, then lateral movement, with timing that reflects an operator’s working hours and cognitive load. Carbonato scans for new hosts every five minutes regardless of time zone. ClosedQuorum polls for its next action on a randomised five-to-fifteen-minute cycle. Neither waits for an operator to be present. That compresses the window between initial access and damage in ways that existing detection logic is not calibrated to catch.
Read the Full Investigation
The full Dispatch article covers the technical architecture of each family in greater depth, discusses the detection implications in detail, and examines what the documented escalation means for defenders building controls today. You can read it here: https://www.anomali.com/blog/malware-gets-a-brain-how-ai-decision-making-is-replacing-hard-coded-c2-logic.
Leave a Reply